Versa GRC — compliance platform
Versa GRC: centralised management of risks, incidents, assets and compliance in line with NIS2, ISO/IEC 27001 and NIST.
Cybersecurity today is not just a technical issue — it is a system of governance, risk control and regulatory compliance. Versa GRC (Governance, Risk and Compliance) is a platform developed by VersaIntel that brings security risks, incidents, assets, audits and compliance requirements together in one place.
Instead of spreadsheets, e-mails and scattered documents you get one structured system — with a clear picture for both security specialists and management.
From fragmented security management to one clear, structured system.
What the platform looks like
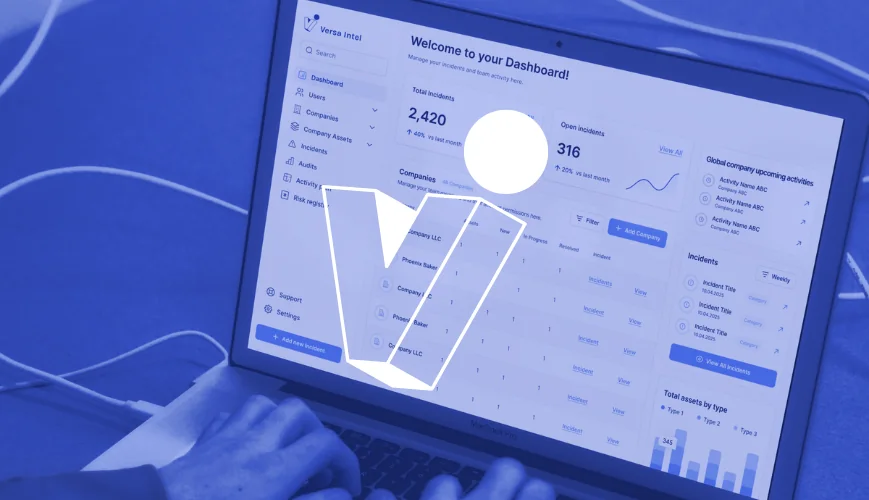
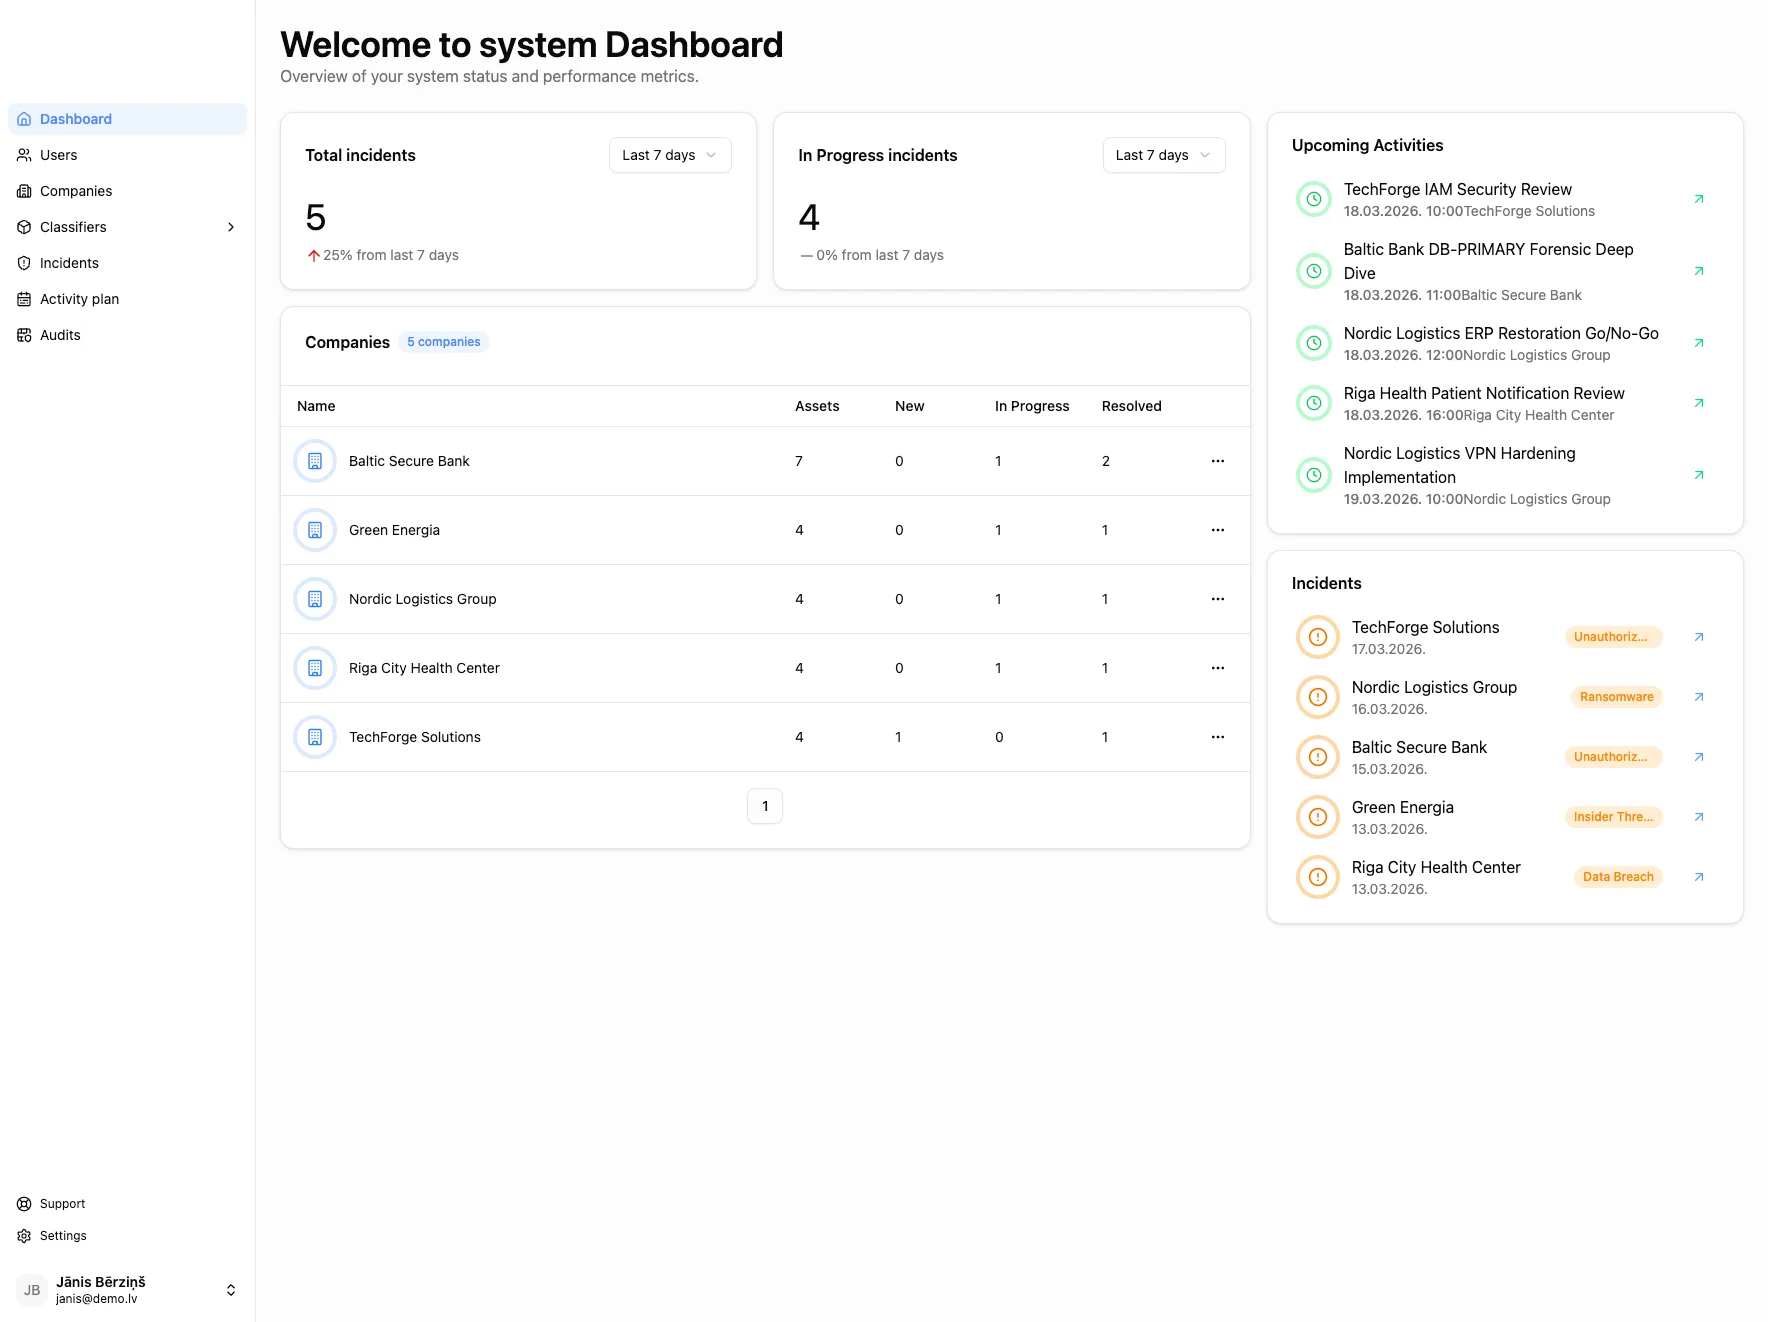
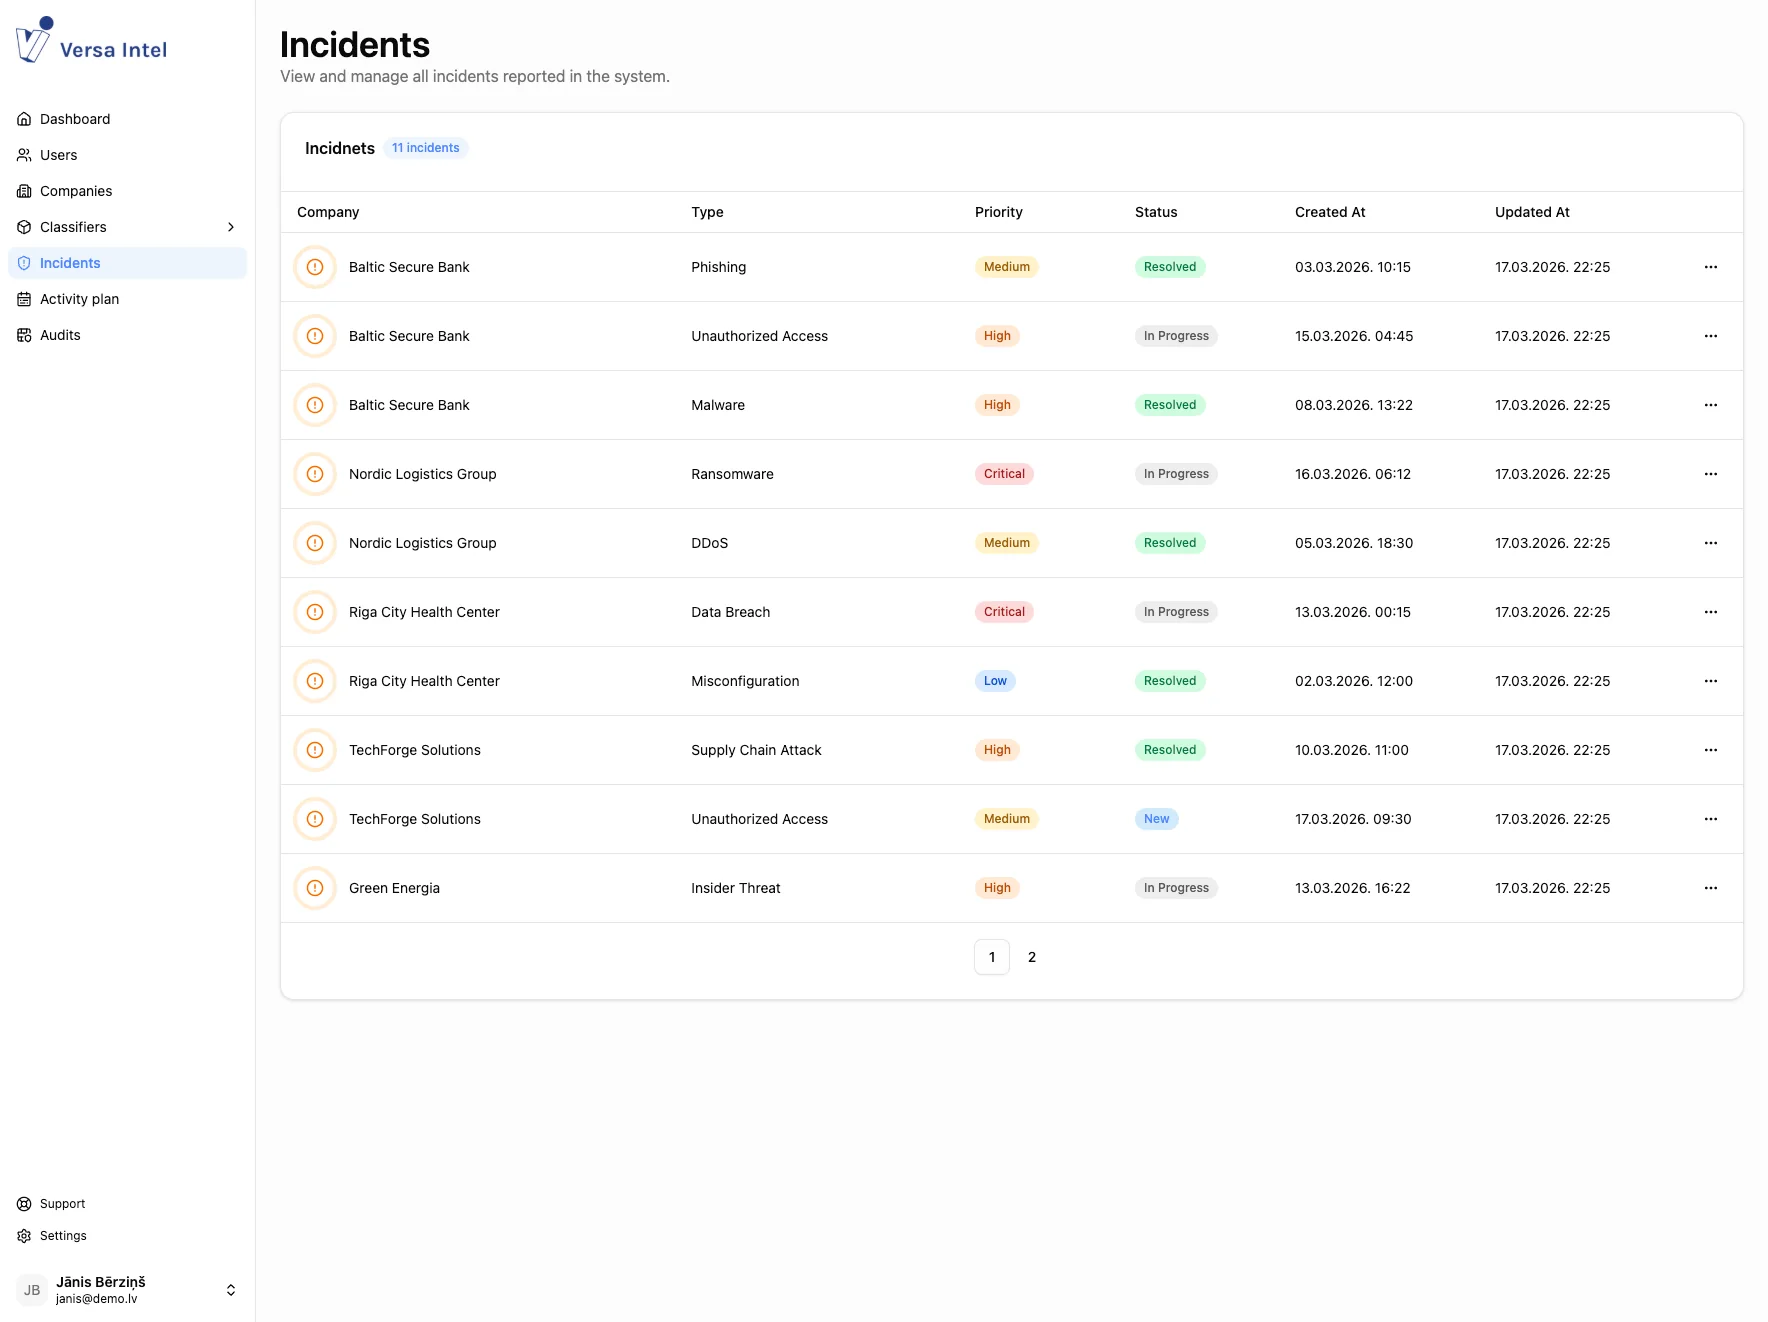
The dashboard shows your organisation’s security posture in real time, and the incidents view shows the status and progress of every incident.
Deployment: in the cloud or on your premises
- SaaS — the platform is available as a cloud service, with no infrastructure to maintain on your side; data is stored in a data centre in Europe;
- In your infrastructure — if your security policy requires it, Versa GRC can be deployed inside your organisation.
One company or several
Versa GRC can be used to manage just your own organisation, or several companies in one place — for example a group of companies or subsidiaries — with a combined view of their security posture.
How Versa GRC works
- Versa SOC — threats generated automatically, plus incident management
- Indicators of compromise (IoC) and threat intelligence
- Microsoft Active Directory access management
- 01Assets
- Inventory of IT and information assets
- Assets linked to risks and incidents
- 02Risks
- A structured, continuously maintained risk register
- Risk assessment and status
- 03Incidents
- Recording and investigation
- Linked to the risk register
- Automatic documentation
- 04Actions and audits
- Corrective actions and their follow-up
- Audit process management
- Security activity planning
- 05Reports
- Real-time dashboard
- Security and compliance reports
- Reports for supervisory authorities
Requirements Versa GRC helps you meet
- NIS2EU directive on cybersecurity risk management and incident reporting
- NKDLRequirements of Latvia’s National Cybersecurity Law
- MK 397Cabinet Regulation “Minimum Cybersecurity Requirements”
- ISO/IEC 27001Information security management system
- NISTInternationally recognised cybersecurity framework
What Versa GRC gives each role
Management
- Real-time view of the organisation’s security posture
- Better prepared for regulatory inspections
- A clear picture for decisions
Security lead (CISO)
- Risks, incidents and assets in one system
- Less manual documentation
- Automated incident reporting
Audit and compliance
- Audit process and corrective action follow-up
- Lower compliance and audit risk
- Structured documentation for inspections
Frequently asked questions about Versa GRC
01How does Versa GRC help with compliance?
The platform links asset and incident management to a risk register, lets you track the status of risks and manage corrective actions. It supports requirements arising from ISO/IEC 27001, the NIS2 Directive, the NKDL and Cabinet of Ministers Regulation No. 397 “Minimum Cybersecurity Requirements”.
02Can Versa GRC be deployed in our own infrastructure?
Yes. Versa GRC is available as a cloud service (SaaS), but if your security policy requires it, the platform can also be deployed in your organisation’s infrastructure.
03Where is the data stored?
In the SaaS version, data is stored in a data centre in Europe. If needed, the platform can also be deployed in your own infrastructure — then the data stays inside your organisation.
04Can the platform manage several companies?
Yes. Versa GRC can be used to manage just your own organisation, or several companies in one place, such as a group of companies or subsidiaries.
05Which systems does Versa GRC integrate with?
The platform can be integrated with security monitoring and cyber intelligence solutions — for receiving and processing indicators of compromise (IoC), using threat intelligence and incident reporting processes. Access management can be integrated with your identity systems, such as Microsoft Active Directory.
06How does Versa GRC work with Versa SOC?
For clients using both Versa SOC and Versa GRC, threats are generated automatically in the platform, where incident management also takes place.
07Can the platform prepare reports for supervisory authorities?
Yes. Versa GRC automates incident documentation and the preparation of reports for supervisory authorities, reducing manual work and helping you report on time.
08Can we see the platform before deciding?
Yes — book a demo and we will show you how Versa GRC would work in your organisation.
Full portfolio of cybersecurity services

NIS2 and NKDL compliance
Who Latvia’s National Cybersecurity Law and NIS2 apply to, what the obligations are — and how to implement them so they genuinely strengthen your security.
Learn more 02
Cybersecurity management (CISOaaS)
Chief Information Security Officer as a service: cyber risk management, security policies, ISO 27001, NIS2 and NKDL compliance.
Learn more 03
Cybersecurity audit
A cybersecurity audit identifies vulnerabilities, assesses cyber risks and delivers prioritised security improvements based on international methodologies.
Learn more 04
Security Operations Center (SOC 24/7/365)
Versa SOC — 24/7/365 cybersecurity monitoring, threat intelligence and incident response.
Learn more 05IT platform security
Secure IT platforms from the ground up: secure architecture and configuration of servers, cloud platforms, networks and Microsoft environments, plus business continuity.
Learn more 06
Cyber incident investigation
Cyber incident forensics (DFIR): an evidence-based understanding of what happened, how and with what impact — and clear next steps.
Learn more 07
Microsoft 365 services for businesses
Microsoft 365 licensing, implementation, configuration, Defender security and maintenance — from a Microsoft partner.
Learn more 08
IT infrastructure security
Managed 24/7 threat protection: endpoint protection, EDR and a SOC in one system that spots attacks early and stops them before they affect the business.
Learn more 09
Data backup and recovery
Backups you can actually recover from: a secure 3-2-1 architecture, automated backups, monitoring and regular recovery testing.
Learn moreWe will help you
Write to us with your requirements, and our representative will contact you as soon as possible.